- Published on
A fresh server was scanned 74 seconds after boot
- Authors

- Name
- AbnAsia.org
- @steven_n_t
Listen to this article · A fresh server was scanned 74 seconds after boot
0:00 / 0:00
Watch this article · A fresh server was scanned 74 seconds after boot
A fresh Ubuntu instance, a public IP, the cloud security group left open and the host firewall switched off. Two services running: SSH with key-only authentication, and a default Nginx page.
The first automated login attempt arrived 74 seconds after boot.
What arrived, and in what order
The attempts were not clever. A dictionary of usernames, turned continuously: root, admin, user, test, support, postgres — and, more revealingly, sol and solana, because a cryptocurrency node is a machine worth taking and there are enough of them to be worth guessing at.
Alongside SSH, scanners probed ports that are almost never deliberately exposed and almost always found anyway: Telnet on 23, Windows RDP on 3389, Redis on 6379, and the Docker API on 2375 — an API that, when reachable, is not a foothold but a full shell.
Then the domain resolution went up, and with it a TLS certificate. Certificate Transparency logs are public by design, so a new name is announced to anyone watching. Within minutes the webserver was being asked for .env, for .git, and for paths that only exist in known vulnerable software.
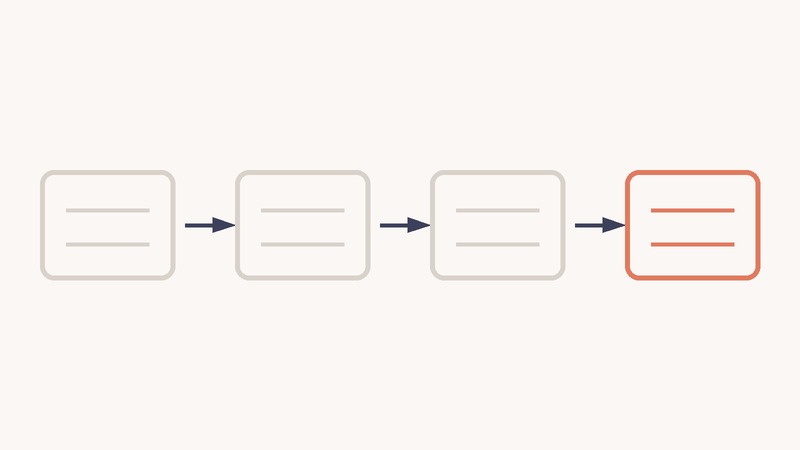
Boot
A new instance answers on the internet. Nothing has been configured yet.
74 seconds
The first SSH login attempt. The sweep does not wait for you to finish.
A certificate
CT logs publish the new name, and the traffic changes character: now it is looking for files.
A day later
9,000 attempts from 127 addresses. None of them knew what the server was.
Why this is not about you
Nothing in the log suggests a person decided to attack that machine. The scanners are unselective: sweep the address space, connect, guess, move on. The output is a constant grey noise that every public IP receives, and the only interesting number is the delay between "reachable" and "probed" — which is now measured in seconds.
That is the part people misread. A quiet log feels like safety, and a fresh server feels like nothing worth attacking. Both impressions are wrong, and they are wrong in the same direction: exposure is the event, not the intrusion.
The five things that would have changed it
The experiment's own server was not compromised, because password logins were disabled from the start. That single decision is why the story is a measurement rather than an incident.
The baseline is short enough to do before the machine is reachable:
Close the ports
Security group and host firewall both default-deny, then open 22, 80 and 443 deliberately.
Keys only
PasswordAuthentication no, PermitRootLogin no. A dictionary stops mattering.
Ban the repeaters
Fail2ban turns thousands of attempts into a short ban list and a readable log.
Bind to localhost
Redis, Postgres and the Docker API never listen on a public interface.
Deny the obvious paths
Block .env and .git at the webserver, and let unattended-upgrades run.
What the 74 seconds is really telling you
There is a version of this story that is about attackers, and it is the less useful one. The more useful version is about the gap between provisioning and configuration: a server is exposed at the moment it can answer, which is minutes before it is ready to be exposed.
Every cloud console makes that gap easy to fall into. The instance comes up with a public address, a default security group and a working SSH daemon, and the operator's next hour is spent installing things rather than closing doors. For 74 seconds, and then for as long as it takes, the machine is a candidate.
The practical conclusion is unglamorous: treat hardening as part of the provisioning step, not the day after. The cost is twenty minutes. The alternative is discovering the gap from a log line, or from someone else.
Source: the recorded experiment "I Put a Server Online. It Got Attacked in 74 Seconds" and its accompanying write-up; figures are the experimenter's own log counts (74 s to first attempt; ~9,000 failed logins from 127 addresses in 24 hours). Hardening guidance cross-checked against standard Ubuntu practice.
Contact: [email protected]